Shared-device session testing for a small SaaS app
A scoped shared device session testing workflow with synthetic conditions, expected outcomes, evidence checks and practical next steps.
Direct answer
For shared device session testing, use a reproducible fixture, explicit expected outcomes and evidence of the final business state. Distinguish a visual cache from an authenticated session, and include local storage in the reproduction.
This is a scoped method for a founder or agency reviewing an existing app or integration. It defines test expectations; it does not describe an audit performed on a client system.
Define the fixture and policy
Two synthetic users share one browser profile and switch accounts after logout.
Use an authorized test environment and synthetic records. Record the release, identities, initial state and dependency conditions. Replace the example policy with your approved product policy before running the checks. If the required outcome is undecided, resolve that decision before classifying the implementation as defective.
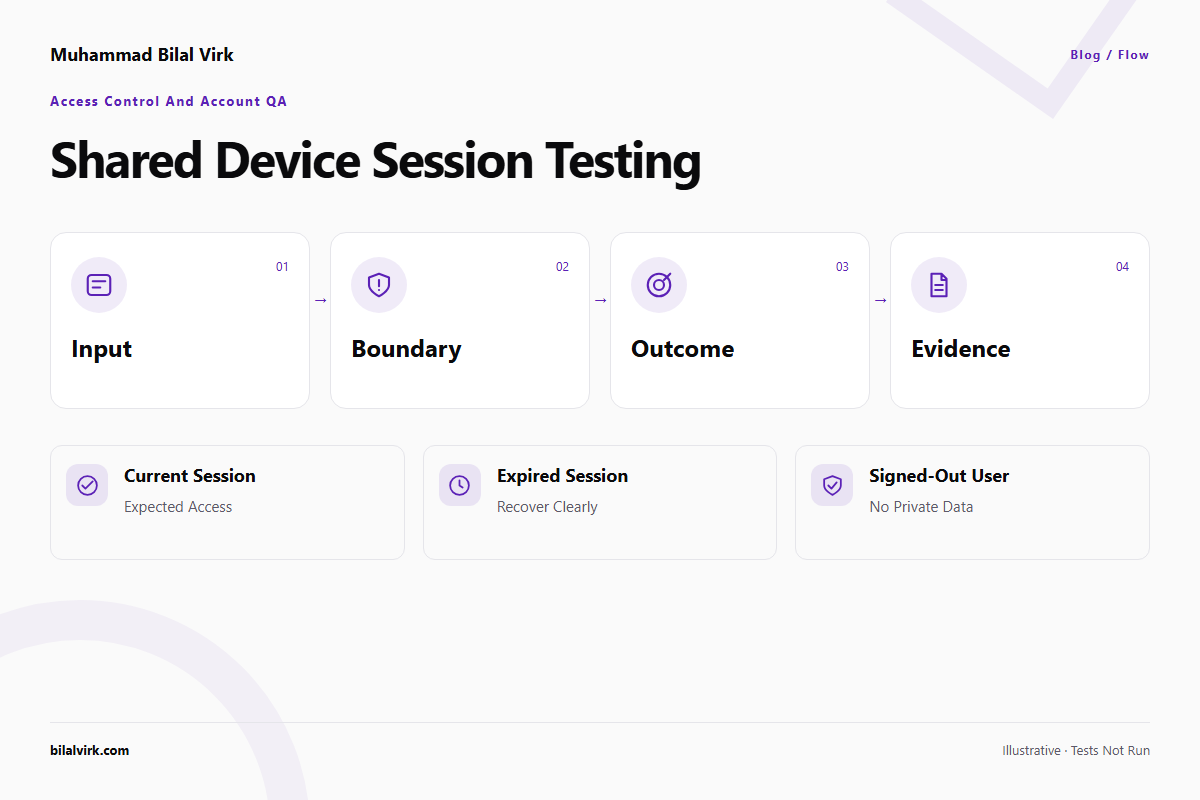
Worked example and acceptance matrix
| Condition | Agreed expectation | Evidence to inspect |
|---|---|---|
| Logout | Old protected requests fail | API response |
| Account switch | Previous private content disappears | Page and storage state |
| Back navigation | No usable prior account session returns | Fresh protected request |
All rows begin NOT RUN. The expectations belong to this example, not every product or provider. Preserve fail and blocked results rather than counting an unavailable dependency as a pass.
Run the conditions independently
1. Logout
Set up this condition deliberately rather than waiting for it to occur during an ordinary click-through. For this fixture, the acceptance condition is old protected requests fail. Capture api response and compare it with the agreed initial state. A different result needs a reproduction record; missing access to that evidence makes the case blocked. Keep the condition separate from the other rows so one successful case cannot conceal a failure here.
2. Account switch
Set up this condition deliberately rather than waiting for it to occur during an ordinary click-through. For this fixture, the acceptance condition is previous private content disappears. Capture page and storage state and compare it with the agreed initial state. A different result needs a reproduction record; missing access to that evidence makes the case blocked. Keep the condition separate from the other rows so one successful case cannot conceal a failure here.
3. Back navigation
Set up this condition deliberately rather than waiting for it to occur during an ordinary click-through. For this fixture, the acceptance condition is no usable prior account session returns. Capture fresh protected request and compare it with the agreed initial state. A different result needs a reproduction record; missing access to that evidence makes the case blocked. Keep the condition separate from the other rows so one successful case cannot conceal a failure here.
Save a reproducible test record
The following original fixture can be copied into a test plan. Its identifiers are synthetic. It contains no production credentials and does not make network requests.
{
  "example": "synthetic; not executed",
  "scope": "Two synthetic users share one browser profile and switch accounts after logout.",
  "cases": [
    {
      "id": "day-37-case-1",
      "condition": "Logout",
      "expected": "Old protected requests fail",
      "evidence": "API response",
      "status": "NOT RUN"
    },
    {
      "id": "day-37-case-2",
      "condition": "Account switch",
      "expected": "Previous private content disappears",
      "evidence": "Page and storage state",
      "status": "NOT RUN"
    },
    {
      "id": "day-37-case-3",
      "condition": "Back navigation",
      "expected": "No usable prior account session returns",
      "evidence": "Fresh protected request",
      "status": "NOT RUN"
    }
  ]
}
Add the actual result, a redacted evidence reference and the environment after execution. Reset state between cases that mutate records. When a response is uncertain, inspect the business receipt or persisted state before repeating the action.
Interpret the result and choose the next step
Distinguish a visual cache from an authenticated session, and include local storage in the reproduction.
A failure report should name the affected condition, the observed difference and its business impact. A blocked result should name the missing dependency and its owner. After a repair, rerun the original failure and a relevant ordinary path against the new release. Keep untested conditions visible. This matrix does not establish exhaustive security, compliance, performance or integration coverage.
Use the paired tool
Authentication Test Checklist provides a practical companion. Its dated enhancement is logout and session switch cases. The planning worksheet creates named cases and exports your recorded outcomes; it does not automatically exercise your app. Use the tool's existing calculation or validation separately where relevant.
Related implementation context: How an AI Voice Agent for Small Business Can Replace Your Front Desk (Without the Overhead); Make.com vs Zapier for Small Business: Which One Actually Saves You More Money.
Implementation reference
Consult Supabase authentication reference for the underlying platform or method. The source is an implementation reference; the fixture and product expectations above are original illustrative conditions, not quoted provider guarantees. Confirm the documentation for your deployed version before implementation.
Frequently asked questions
What demonstrates logout?
For this fixture, old protected requests fail. Inspect api response; a success message alone may not establish the approved outcome.
What if account switch cannot be reproduced?
Record it as blocked with the missing setup or dependency. Do not replace the missing evidence with the image or a generated expectation. The diagram is instructional, and this article reports no executed result.
When is a scoped review useful?
Request one when a critical condition fails, ownership is unclear or the team cannot determine what committed. Bring the reproduction and agreed policy.
Recommended action
Start with the matrix for shared device session testing, then record evidence before accepting or repairing the result. Discuss a scoped AI app audit or book a discovery call. Share the stack and broken journey in the initial enquiry; arrange any required access separately.
Want this built against your real numbers?
A 30-minute call to scope the workflow, agent, or automation you actually need.